0:13
Sys 01 · Queue (own operations)
Eight channels, one person, no lost message
Requests arrived in eight channels, and the ones nobody saw for an hour were the ones that mattered. Every message now becomes a job an agent picks up, runs, and answers in the channel it came from. One relay process holds the lock, so a second copy exits, and a worker that dies leaves its job still marked as running with the start time beside it. A message that already became a job is never queued twice, and nothing sweeps a stalled job automatically, so the start time is what I look at in the morning.
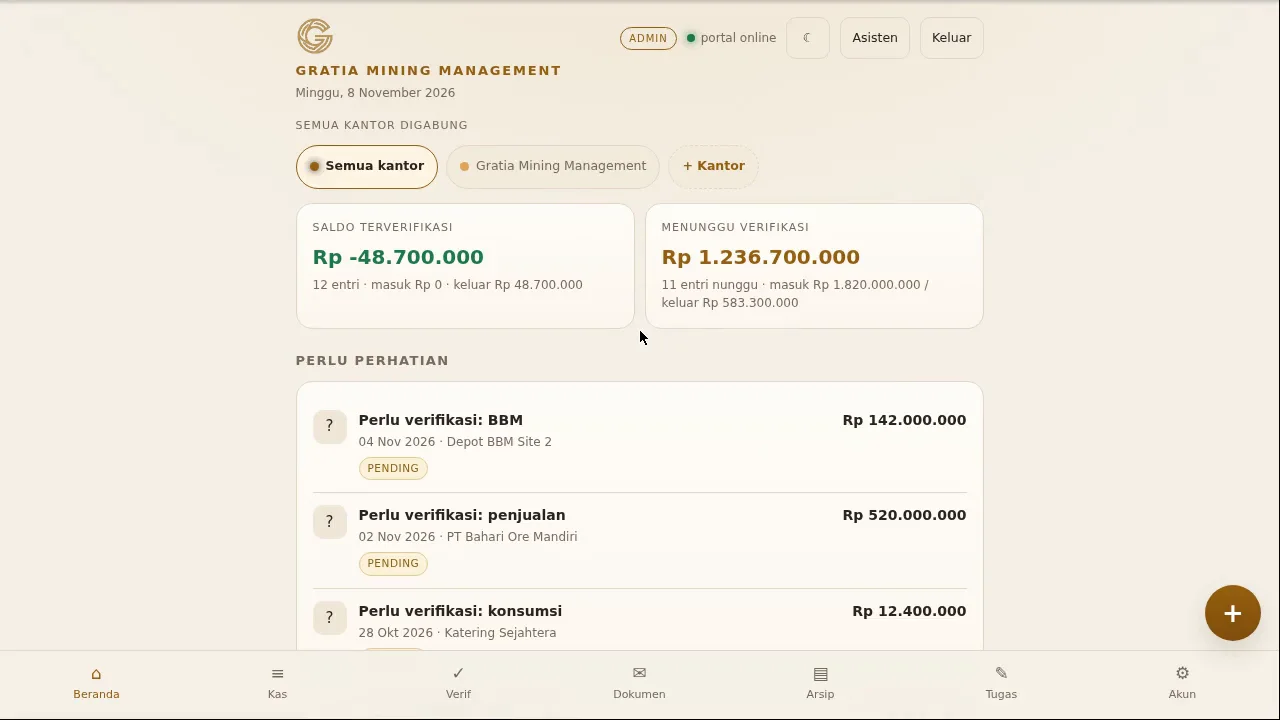
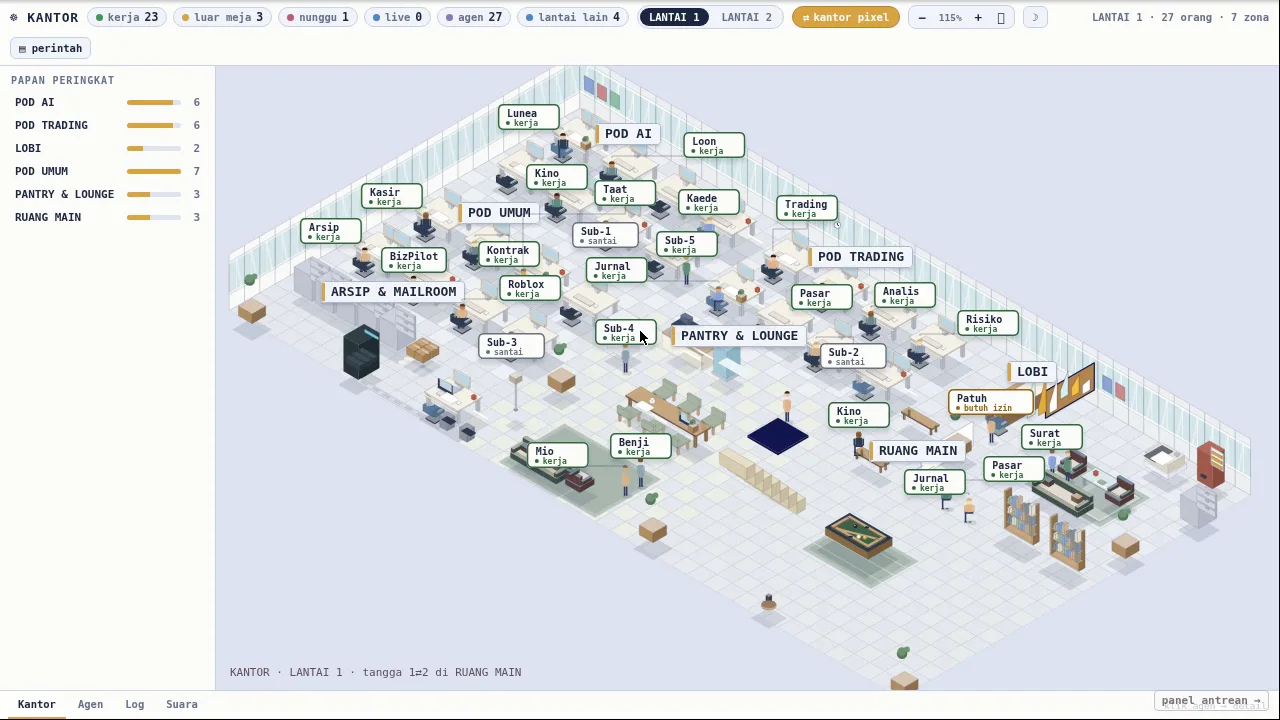
verified Eight channel ids, one lock file, and a clip of the queue running on this machine.
Live queue